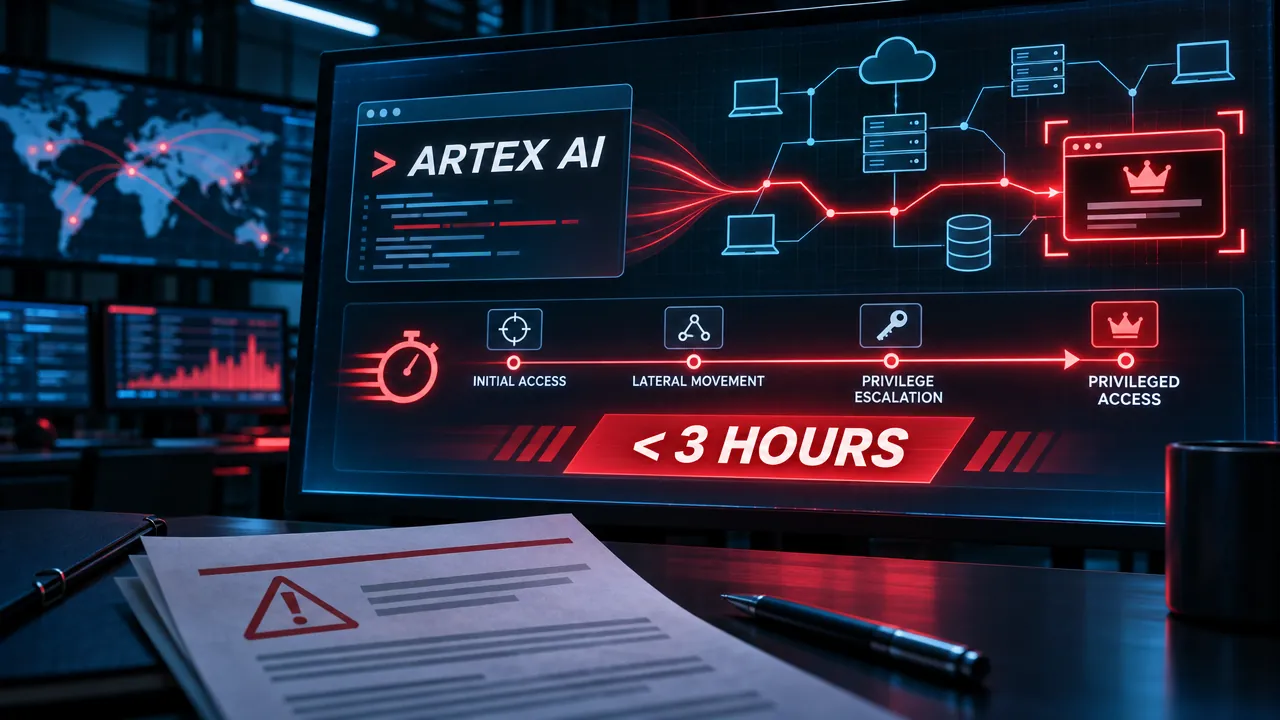
The FBI says attackers used ARTEX, an open-source AI-powered penetration-testing framework, to automate parts of network intrusions and reach privileged access in some cases in under three hours. Organizations should check for exposed ARTEX consoles, secure credentials, and investigate unusual access to AI services.
Key takeaways
- The FBI says attackers used ARTEX to automate parts of reconnaissance and intrusion, reaching privileged access in some cases in less than three hours.
- The FBI reported finding more than 1,600 ARTEX consoles exposed to the public internet by early November.
- Reporting linked ARTEX-related attacks to stolen personal data belonging to at least 68,000 people in South Korea and access to Microsoft 365 environments associated with at least 2,250 ConnectWise customers.
- The original ARTEX GitHub repository was removed by its developer, but reported copies and forks may remain available.
- Organizations should inventory internet-facing systems, secure or remove exposed consoles, rotate potentially exposed keys, and review credential and permission changes.
The FBI says attackers using ARTEX, an open-source AI-powered penetration-testing framework, reached privileged access in some network intrusions in less than three hours. The warning highlights how tools designed to automate security testing can also help criminals move quickly through exposed systems.
ARTEX has been linked in reporting to attacks against South Korean financial institutions and a breach affecting ConnectWise customers. The incidents show why organizations need to check not only for vulnerable applications, but also for exposed tool consoles and credentials that attackers can use to access AI services.
What the FBI Says Attackers Did With the Open-Source Tool
The FBI says criminals used ARTEX to automate parts of network reconnaissance and intrusion. In some cases, attackers reportedly obtained privileged access in under three hours - leaving defenders a narrow window to spot and contain suspicious activity.
The tool’s open-source nature means its capabilities are not limited to its original developers. After reports of malicious use, its developer removed the original GitHub repository. However, copies and forks reportedly remain available, so removing the original source has not necessarily made the tool inaccessible.
The FBI also reported finding more than 1,600 ARTEX consoles exposed to the public internet by early November. An exposed console can provide an entry point for attackers, particularly if it is unprotected or configured with weak credentials.
Reported Victims Include South Korean Institutions and ConnectWise Customers
Reported attacks on South Korean financial institutions resulted in the theft of personal data belonging to at least 68,000 people. In a separate incident, attackers compromised ConnectWise and accessed Microsoft 365 environments associated with at least 2,250 customers.
The activity attributed to ARTEX is part of a wider pattern of AI-assisted cyberattacks. CrowdStrike has reported that China-linked hackers targeted more than 200 organizations using the tool. Microsoft has also tracked related activity involving the group it calls Storm-0940. These reports describe different investigations and should not be read as evidence that every incident had the same operators or methods.
Why Exposed Consoles and Stolen API Keys Raise the Risk
The risk extends beyond a publicly reachable ARTEX console. Amazon has described cases in which attackers used stolen AI API keys to access AI models, then directed agents to search for additional keys. This could help criminals expand access if exposed credentials are found in applications or cloud environments.
There is an important qualification: Amazon said it did not observe the attacks directly and could not independently verify the outcomes recorded in the activity it reviewed. The account points to a potential way stolen keys may be abused, but it should not be treated as independent confirmation of every reported result.
What Organizations Should Check Now
Organizations should inventory internet-facing applications and look for exposed ARTEX consoles, unauthorized services, and secrets embedded in code or configuration files. If a key may have been exposed, revoke and rotate it, then check where it was used.
Security teams should also review recent changes to application credentials and permissions, including unexpected new keys, elevated privileges, or unusual access to AI services. Compare those changes against deployment records and investigate activity that cannot be tied to an authorized user or process.
The practical response is to reduce what attackers can reach and how long they can use compromised access: identify exposed systems, remove or secure them, and monitor credential and permission changes. Organizations should follow official FBI guidance for relevant indicators and response updates.
By the numbers
More than 1,600 ARTEX consoles were exposed to the public internet by early November.
The FBI reported this figure in its warning, as described in the article. The article does not specify a year for the early-November observation.
At least 68,000 people had personal data stolen in reported attacks on South Korean financial institutions.
This figure comes from reporting on the attacks cited in the article; it is not presented as a count independently verified by the FBI.
Microsoft 365 environments associated with at least 2,250 ConnectWise customers were accessed in a separate incident.
The article describes this as a reported incident and does not establish that it had the same operators or methods as every other ARTEX-linked attack.
CrowdStrike reported that China-linked hackers targeted more than 200 organizations using ARTEX.
This figure reflects CrowdStrike's reporting. The article distinguishes that investigation from other reported incidents and does not attribute every attack to the same group.
Step by step
- 01
Inventory internet-facing systems
Identify public-facing applications, services, and management consoles, then check whether any ARTEX instances or unauthorized services are reachable from the internet.
- 02
Secure or remove exposed consoles
Disable services that are not needed. For required services, restrict network access and enforce strong authentication and approved configuration.
- 03
Find and rotate exposed secrets
Review code, configuration files, and cloud environments for exposed API keys or credentials. Revoke and replace any potentially compromised secrets.
- 04
Review credential and permission changes
Look for unexpected keys, privilege elevations, and unusual access to AI services. Compare each change with deployment records and authorized activity.
- 05
Investigate and monitor suspicious activity
Investigate access that cannot be tied to an authorized user or process, and follow official FBI guidance for relevant indicators and response updates.
Frequently asked questions
What is the ARTEX AI hacking tool?
ARTEX is an open-source, AI-powered penetration-testing framework that the FBI says criminals used to automate parts of network reconnaissance and intrusion. Its security-testing capabilities can be misused, and copies or forks reportedly remain available after the developer removed the original GitHub repository.
How quickly did attackers using ARTEX reach privileged access?
The FBI says attackers reached privileged access in some intrusions in under three hours. That reported speed leaves defenders a narrow window to identify and contain suspicious activity, though it does not mean every attack followed the same timeline.
How many ARTEX consoles did the FBI find exposed?
The FBI reported finding more than 1,600 ARTEX consoles exposed to the public internet by early November. A publicly reachable console may increase risk, particularly if it lacks protection or uses weak credentials.
What should organizations do if an AI API key may be exposed?
Organizations should revoke and rotate the potentially exposed key, then investigate where and how it was used. They should also review related credentials, permissions, and access to AI services for unexpected changes or activity.